Built-in security
Protecting the platform that monitors the infrastructure: access, data and operational surface.
The monitoring tool must not become a point of exposure
Sentinet³ is designed to operate in high-security environments, implementing self-protection mechanisms against cyber attacks that limit the exposure of the monitoring system and govern access to the information collected. Platform security covers the web components, privileges, credentials, storage and the execution of services.
These measures ensure operational continuity, data integrity and active protection of the infrastructure, and make the platform suitable for use in military, government, critical or classified environments, including federated architectures.
| Protection area | Mechanisms |
|---|---|
| Access | Two-factor authentication (2FA) for administrators and operational profiles, ensuring secure access even if credentials are compromised. An anti brute force mechanism that automatically detects and blocks repeated unauthorised login attempts. |
| Web applications | Integrated Web Application Firewall (WAF) that inspects, filters and blocks malicious requests to the platform’s web modules. |
| Network perimeter | Natively integrated internal firewall, configurable for segmentation and granular control of traffic between the system’s modules and towards the outside. |
| Data and secrets | Passwords, tokens and access keys handled with up-to-date cryptographic algorithms. Encrypted file system, keeping data confidential even in the event of unauthorised physical access to the device. |
| Configurations | Configuration files accessible only to authorised processes and protected from unauthorised access. |
| Privileges | Hardening that prevents unauthorised privilege elevation by compromised users or processes. |
| Isolation | Each component runs in segregated environments, with sandboxing or containerisation, to prevent the lateral spread of any compromise. |
A critical link in the operational chain
Protecting the console, limiting administrative privileges and keeping credentials robust prevent the monitoring system from becoming a point of exposure itself. The configuration must provide for:
- role-based access profiles;
- protection of communications;
- change control.
Technical and organisational measures. These measures complement, but do not replace, the organisational management of security: policies, segmentation, patch management, backups, audits and operating procedures for the environment.
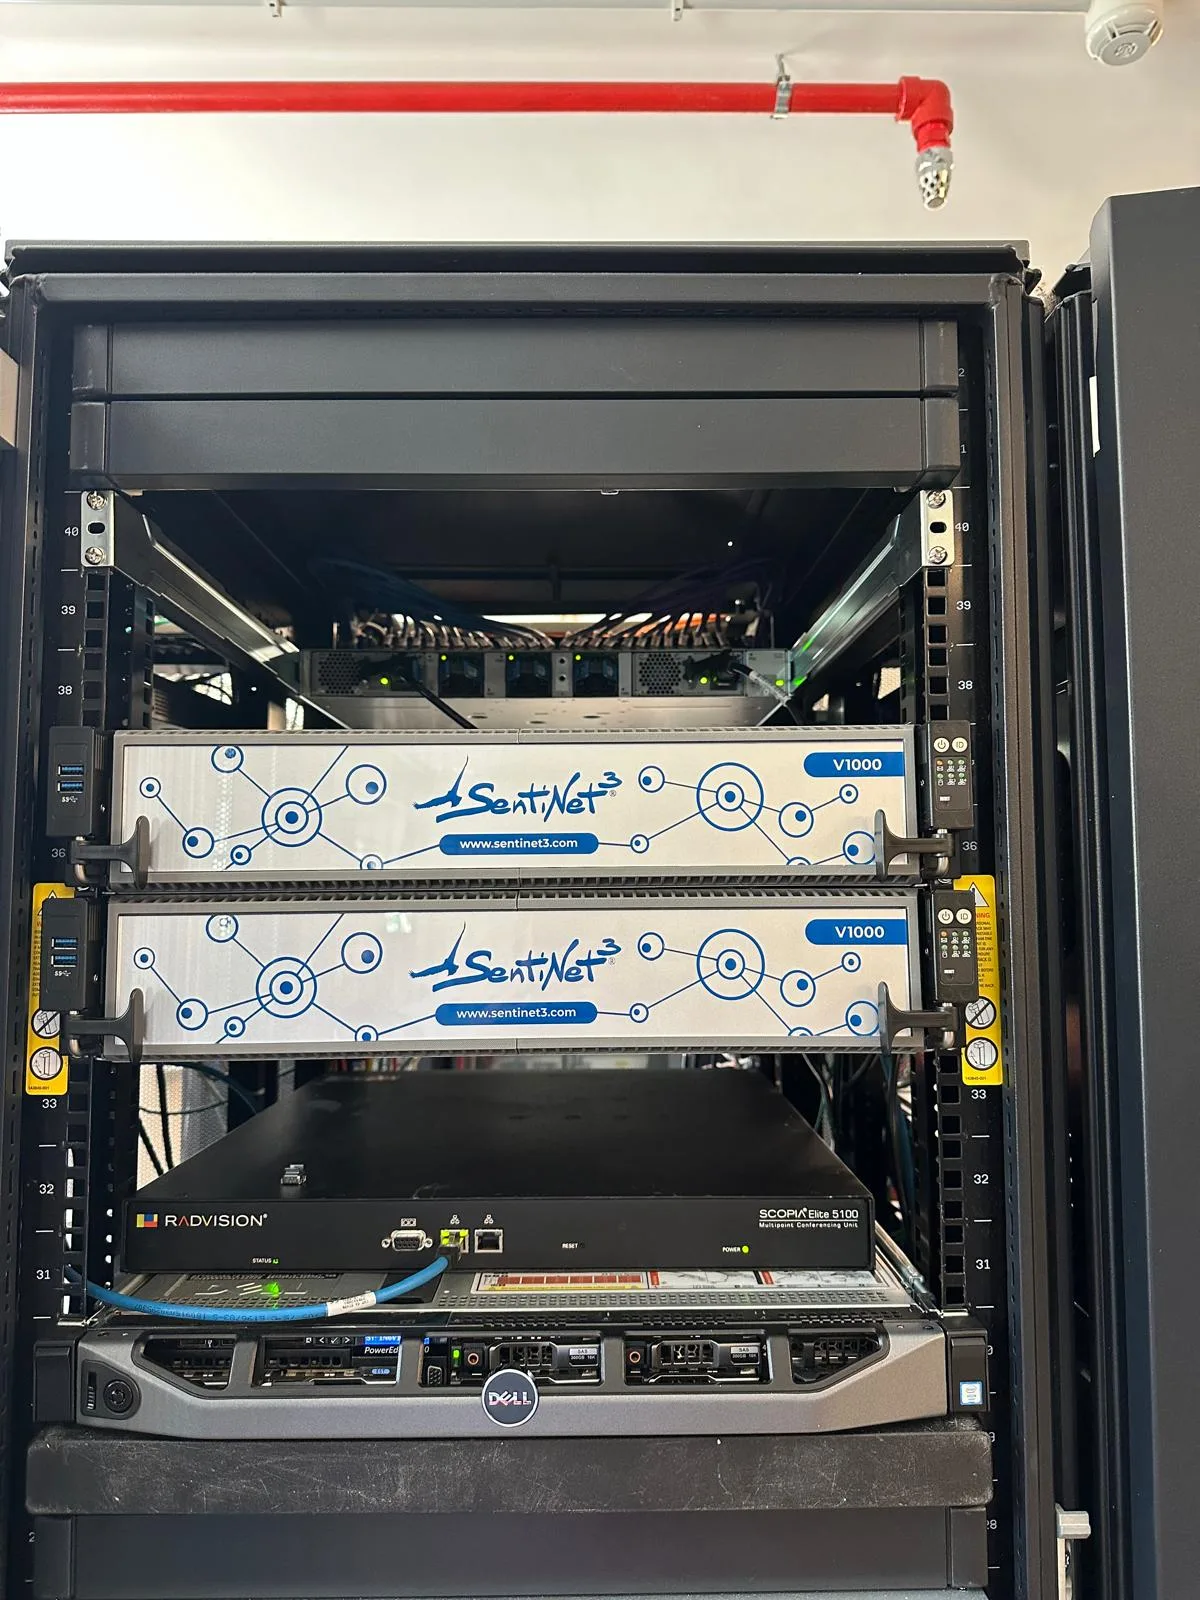
Platform security and infrastructure cybersecurity
Built-in security protects Sentinet³ Core. It is distinct from the functions of the Infinity modules dedicated to the cybersecurity of the monitored infrastructure.
Built-in security
Protects access, data, configurations and components of the monitoring platform.
Infinity modules
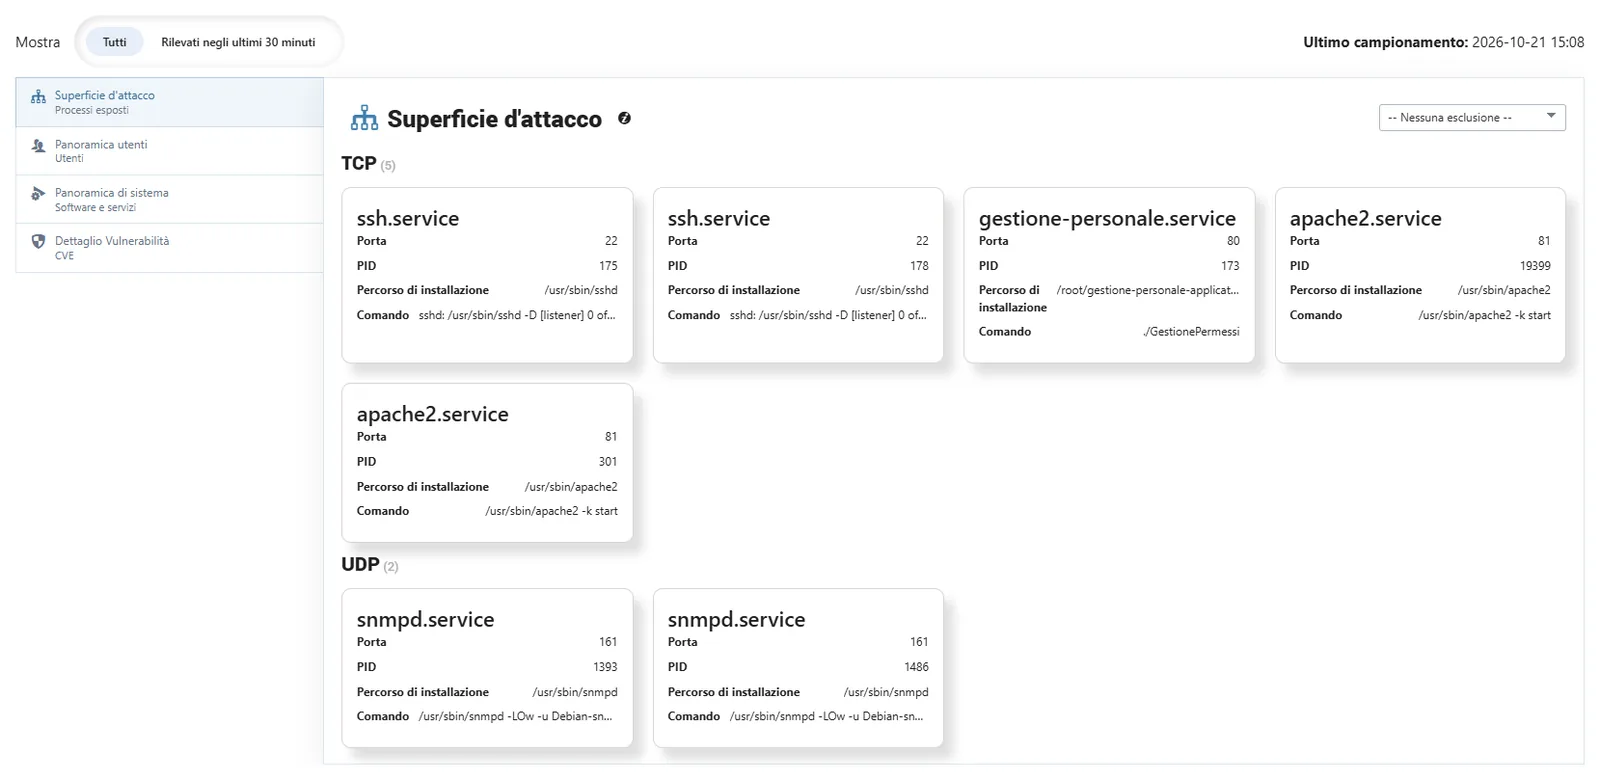
Security Insight and Threat Insight analyse host security, vulnerabilities and attack paths across the infrastructure.
Related topics
Want to see Sentinet³ on your infrastructure?
Tell us about your environment: sites, technologies, critical services. We will show you how Core and Infinity can work on your case.